Ledger 'spy chip' attack: tampered wallets sent recovery phrases over LTE; up to $93 million stolen
Ledger says implants hidden in signers sold by a Southeast Asian reseller read the 24 words off the screen and sent them to an attacker. How to check a hardware wallet you bought in Pakistan.
Ledger has confirmed that some of its hardware wallets were fitted with a hidden "spy" implant that read users' 24-word recovery phrases and sent them to an attacker over a mobile network, the company said on X on Tuesday, CoinDesk reported. On-chain researchers estimate losses of up to $93.2 million across more than 300 wallets, roughly Rs 25.8 billion at today's dollar rate. Ledger has not confirmed a figure.
How the attack worked
Ledger calls it a physical supply-chain attack, not a hack of its software or systems:
- an extra circuit was hidden inside the device's casing;
- when the owner set the wallet up and the recovery phrase appeared on screen, the implant read the words;
- it sent them out over LTE using an eSIM.
The implant did not touch the secure element, the operating system or any transaction. It did not need to: anyone with the 24 words can rebuild the wallet on another device and empty it.
Where the devices came from
Every confirmed loss in the incident that came to light on 9 October involved a signer sold by CryptoBilis, a Southeast Asian reseller, which has stopped selling Ledger devices. On Tuesday Ledger asked sellers in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia and Hong Kong to pause sales and pull stock, Cointelegraph reported. Ledger said "the only confirmed incidents remain contained to Southeast Asia" and that it has "no indication" its own systems or direct sales were compromised.
The worry is spreading: electronics chain MediaMarkt Saturn stopped selling Ledger devices after a customer in Germany reported finding an implant, and rival Trezor has cut back its resellers as a "preventative step". Tether has frozen $10 million in USDT linked to the theft.
If you hold crypto in Pakistan
If your wallet came from a marketplace seller, a reseller or someone who brought it from abroad, rather than from the maker's own store, it travelled through the same kind of chain this attack used.
- Bought from CryptoBilis? Do not set it up. If you already have, move your funds to a new wallet with a newly generated recovery phrase, as Ledger advises.
- Bought from anyone other than the maker? Treat the device with suspicion. The safest course is a new device bought from the maker's own store and a fresh recovery phrase.
- Never use a phrase that came with the device, printed on a card or already filled in. A genuine wallet always creates a new one in front of you.
- Opened box, broken seal or extra weight? Do not use it.
Ledger chief executive Pascal Gauthier said the investigation is still working out "who tampered with these signers or where in the distribution chain it happened".
Frequently asked questions
- Was Ledger hacked?
- Ledger says no: it calls this a physical supply-chain attack in which implants were added to devices sold by a reseller, CryptoBilis, and says its own systems and direct sales were not compromised.
- What should I do if I bought a Ledger from a reseller?
- Ledger advises CryptoBilis buyers not to initialise the device, and anyone who already used one to move funds to a new device with a newly generated recovery phrase.
Sources
Related reading
Crypto
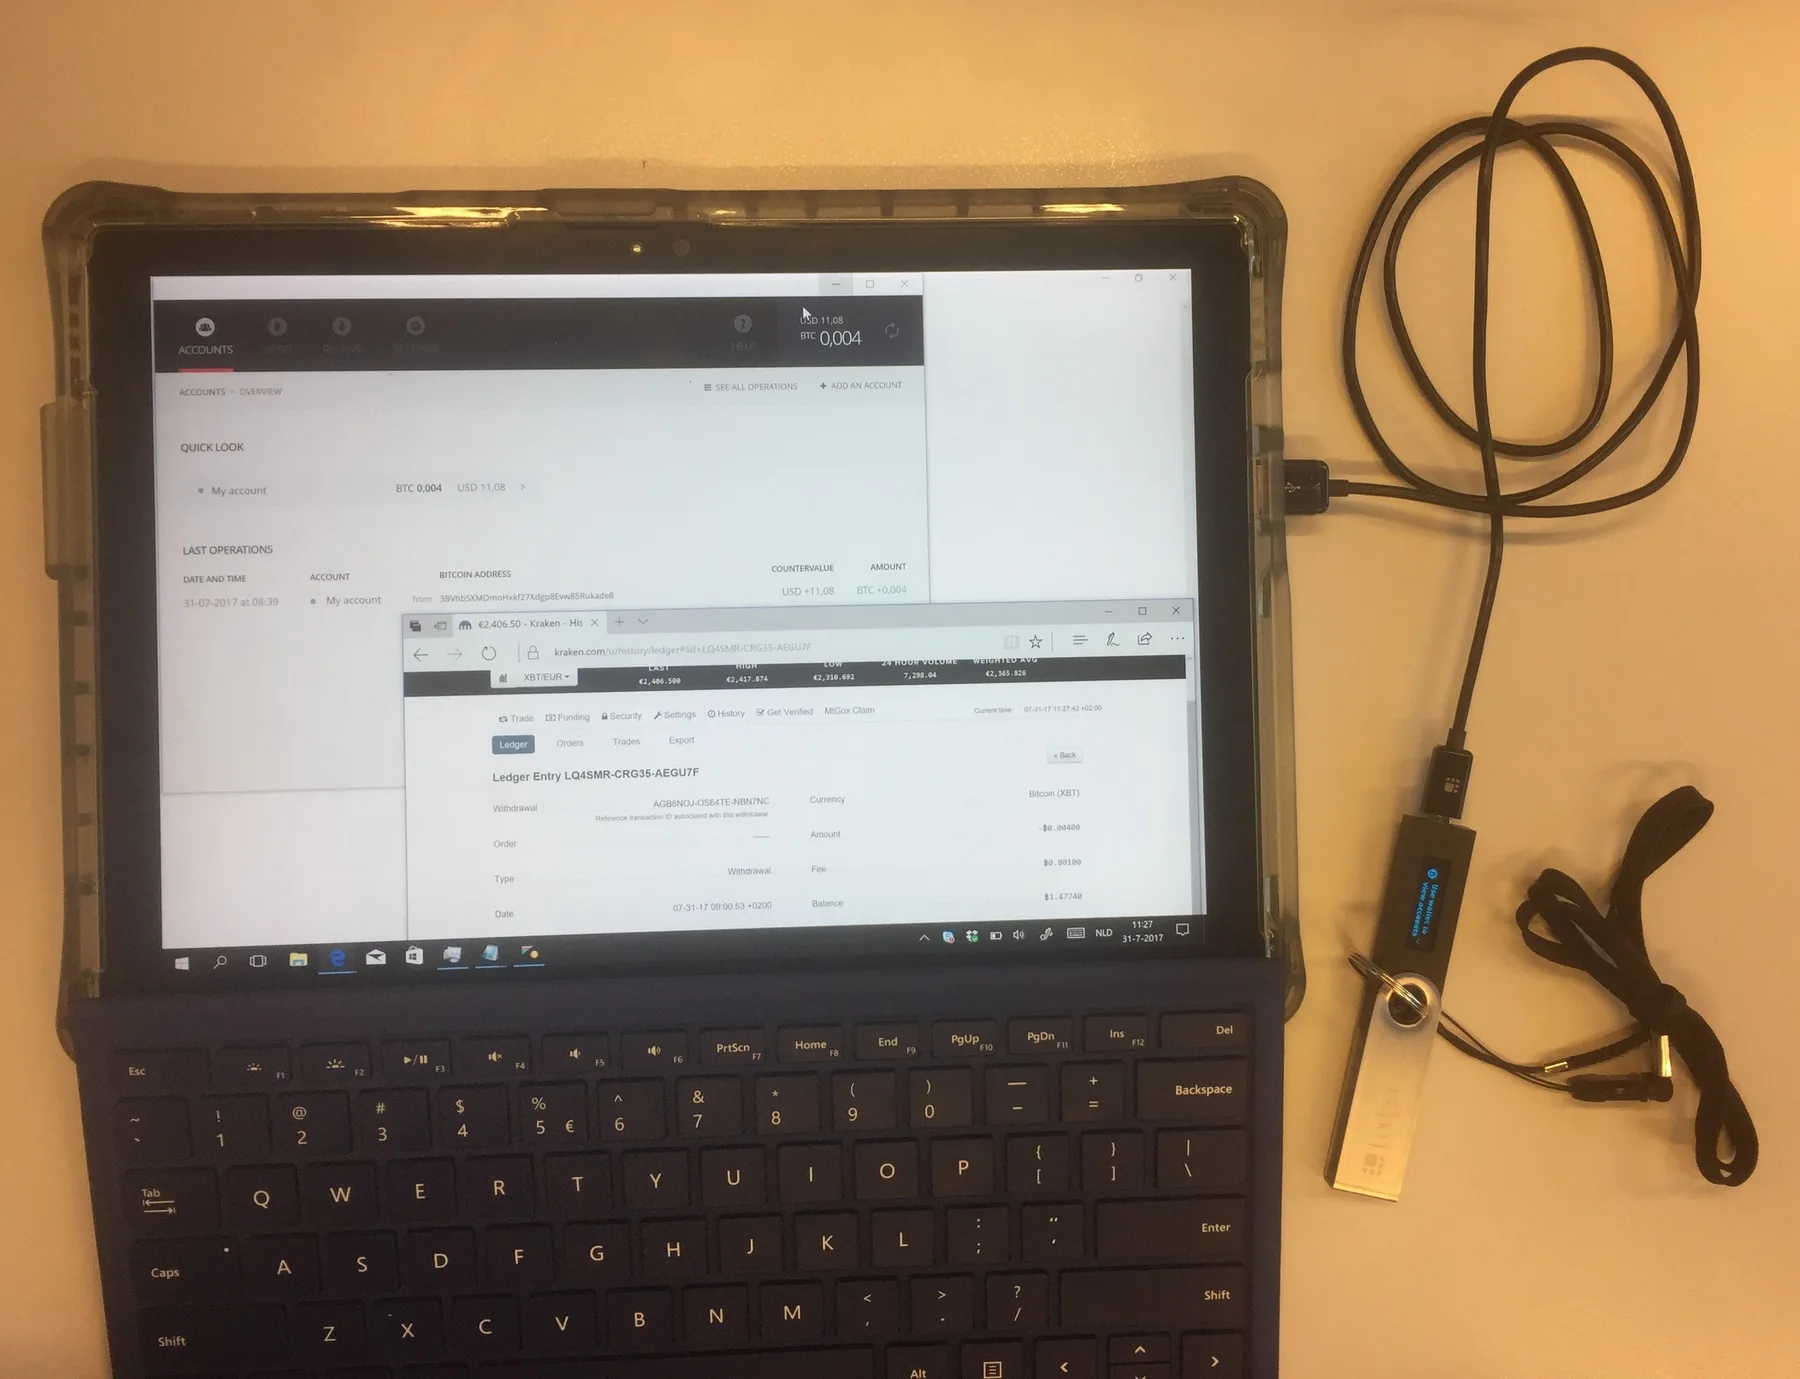
Ledger confirms hardware implant in CryptoBilis-sold wallet; losses may top $86 million
Ledger now says an affected device had an unauthorised implant, the reseller has stopped all sales, and owners of wallets bought there should move funds to a new seed.
4d ago
Crypto
Binance Pool shuts on 10 November: miners must move hashrate and redeem Pool Savings before the deadline
Binance is closing its six-year-old mining pool along with Cloud Mining, Pool Savings and the Transaction Accelerator. Records stay readable until 24 November.
18h ago
Crypto
Bitcoin drops 2.2% toward $82,000 as oil jumps; Strategy adds 250 BTC to 848,250
Attacks on Ukrainian energy sites and a Hormuz tanker fire lifted Brent to $107, and bitcoin gave back its Monday gain. A coin is about Rs 2.29 crore; US inflation data on Wednesday is next.
1d ago
Reader comments 0
No comments yet. Say something useful.